Material Security/Bleeping Computer
Click here to read the entire article
Since mid-August 2026, a phishing operation has been harvesting live Google sessions from corporate users. Every signal defenders usually rely on to judge a link returned a reassuring answer, and the operator built the chain that way on purpose.
Material Security’s Threat Research team identified the campaign and has taken down hundreds of domains used by attackers in what they have dubbed Operation CloudFire. Here’s what they learned along the way.
The lure: Google Calendar invites
The messages arrive as Google Calendar invites, sometimes delivered by BCC and often sent from an organization the recipient has already corresponded with. The pretexts are mundane: voicemail notifications, RFP and RFI requests, court summonses, and missed payment notices.
Most links point to Google itself. The typical pattern is Google’s own /url redirector with the real destination in a query parameter, though other waves used share.google and Drive file links for the same purpose. One variant used Intuit transaction notification links.
In every case, when the message is scored, the domain, certificate, and reputation displayed are legitimate and trusted.
The capture: Reverse proxy in front of a Google sign-in page
The attacker runs a live reverse proxy in front of the genuine Google sign-in page. The victim enters a password, receives a real prompt, and approves it, all while the operator watches the session in real time.
The server relays SMS codes, authenticator codes, Google’s Tap-Yes number matching, and phone-based account recovery to Google as each one arrives, so none of the second-factor controls stop the session from being captured.
The framework behind this, Nyasher, has been documented publicly since February, after a hardcoded key was found in its JavaScript.
Why the controls don’t fire
Reputation systems answer a question about ownership: who registered the domain, what else it has hosted, and whether anyone has complained about it. This campaign was assembled so that those answers were consistently benign, and it has three layers.
The first layer is Google’s redirector. The second is a Cloudflare Turnstile challenge, which in some builds is the genuine widget served from Cloudflare’s own infrastructure. The third layer is the password-capture page itself, which has no static website to scan.
The Javascript constructs it in the browser after the visitor clears the challenge, so a crawler has nothing to fetch and a proxy log has nothing to record. To Material’s knowledge, no one had scanned those pages before the campaign was documented.
The infrastructure is disposable by design. The initially observed campaign used many lure domains across multiple registrars, most registered only days before use. Receiving endpoints were staged one to twenty days ahead of the wave they served.
One wildcard certificate was issued 46 minutes before the domain it covers was registered. Blocking any single component costs the operator a few dollars and an afternoon of work.
Click here to continue reading
Andrew Lepczyk, CreditUnions.com/Callahan
Banking branches are a financial lifeline for a community and a way for credit unions to deepen their relationships with members.
Although physical footprints might seem out of step with today’s preference for digital experiences, branches still offer something a screen can’t: a place to seek advice and navigate complex financial decisions.
- Alaska leads the country in branches per credit union with 11.9. Given the remote nature of the state, many credit unions operate far-flung branches to serve harder-to-reach members.
- For some members of Tongass Federal Credit Union ($251.9M, Ketchikan, AK), the nearest branch can be a plane ride away. Local “microsites” have improved service for those remote locations.
- North Carolina and Florida trail Alaska with 11.2 and 10.2 branches, respectively. Both of these states have large, state-wide credit unions with large branch networks. The states with the fewest branches per credit union include West Virginia with 2.1 and New Jersey at 2.2.
- Access to a physical branch is critical in banking deserts, where limited nearby financial institutions can leave consumers without convenient options for everyday services and face-to-face guidance. The Federal Reserve has found these gaps can be especially harmful to minority communities.
- Great Lakes Credit Union ($1.4B, Bannockburn, IL) teams up with community partners to tackle inadequate access to financial services and improve the quality of life in Chicago’s West Side communities.
- Research from Affinity Plus Federal Credit Union ($5.0B, Saint Paul, MN) shows more than 65% of its members join in person, then return to discuss buying a home or car, opening a checking account, and more. Digital adoption is rising, but branches are a significant source of strategic growth for the cooperative.
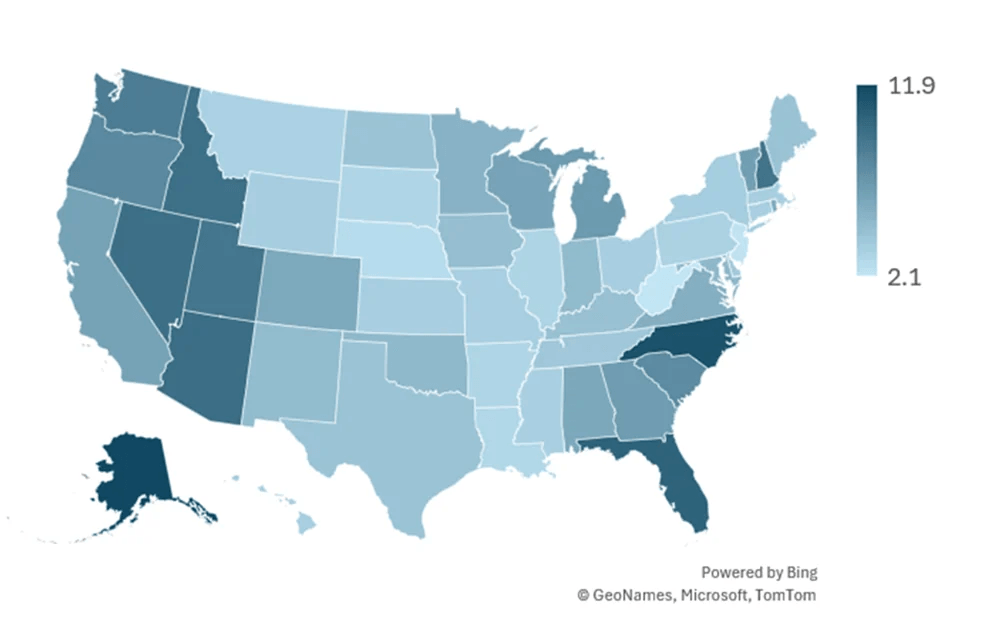
FOR U.S. CREDIT UNIONS | DATA AS OF 06.30.26
SOURCE: CALLAHAN & ASSOCIATES
Esteban Camargo, CUSO Magazine
The recent changes in NCUA leadership with new NCUA Chairman John Crews at the reins have not affected the administration’s efforts at deregulation. Earlier today, the National Credit Union Administration announced its fourteenth round of deregulation proposals as it continues to make efforts towards eliminating cumbersome and unnecessary regulation. As part of the process, NCUA is seeking public comment on the proposed changes, which affect commercial lending, the Paycheck Protection Program (PPP), and statutory liens.
The first of the proposed changes would be to remove 12 CFR 723.9, a provision which was adopted in 2016 for commercial lending. Per the NCUA, “the provision has served its purpose and is no longer necessary. Removing it would reduce regulatory complexity and improve the clarity of NCUA’s regulations.”
The second change makes permanent the regulatory treatment of PPP loans in place since April 2020. The third amends the language of 12 CFR 701.39(a)(1) to remove duplicative language since “credit unions are already responsible for identifying and complying with applicable laws when exercising their statutory lien authority.”
All the proposed changes can be found on the NCUA website through their Deregulation Project page. Since launching in 2025, the project has been focused on removing or amending current regulations that the NCUA has deemed to be obsolete, duplicative, overly burdensome, or guidance within regulation. According to the site, 37 total items have been addressed with 12 finalized rules to date.
defi SOLUTIONS, published on CreditUnions.com
Click here to read the entire article
While affordability remains the top priority, lenders that build trust and blend digital convenience with human support can stand out with today’s borrowers
defi SOLUTIONS, a leading provider of end-to-end, SaaS loan originations, servicing, and managed servicing solutions, today released new research examining how U.S. consumers are approaching borrowing amid continued economic pressure. The survey of 1,500 U.S. consumers ages 18 to 64 examines borrowing attitudes, how consumers choose among lenders, and what they expect from the loan experience.
The research found that the majority of respondents (roughly 53%) are open to taking out a loan in the near term, 22% said they were considering a loan within the next six months, and 20% may take out a loan before the end of 2027. At the same time, 55% said they try to avoid debt whenever possible, suggesting a market where borrowing demand remains significant but consumers are approaching debt with caution.
“Consumer loan demand has been subdued, but our research suggests the tide could be starting to shift,” said Tom Allanson, CEO at defi SOLUTIONS. “More than half of consumers are considering borrowing, and as that demand returns, lenders will be competing for borrowers whose expectations have evolved. Affordability will always matter, but today’s borrower is also shopping around and evaluating the entire experience, from the first interaction to the ease of the digital process to the ability to reach a person when needed. Lenders should be taking a hard look at whether they’re prepared to deliver on those expectations.”
Key findings from the October 2026 report:
- Borrowers are shopping around: Nearly half of respondents (47.3%) compare three or more lenders, and 30.5% compare two. Only 22.1% go straight to one lender.
- Price leads lender selection, but trust matters: When deciding who to borrow from, 46.5% prioritized rate and loan term, while reputation and trustworthiness ranked second at 24.6%.
- First impressions can influence whether borrowers move forward: 61.2% said their first interaction with a lender is “very important,” while another 35.7% said it is somewhat important.
- Consumers favor digital with access to human support: 44.5% prefer a mostly digital application with easy access to a person if questions arise, compared with 17.9% who want a fully digital process with no human interaction, and 24.5% who prefer working directly with someone in person or over the phone.
- Economic pressures are weighing on borrowing decisions: Inflation and the rising cost of living were cited by 41.9% of respondents, slightly ahead of high interest rates at 40.1%. Financial stress was cited by 33.7%, while about one in five respondents expressed concern about not getting approved.
- Vehicle purchases drive borrowing needs: Buying a vehicle was the most common reason for borrowing, cited by 24.3% of respondents, ahead of emergency expenses (12.7%), buying a home (10.9%), and consolidating debt (8.4%).
- Affordability drives loan decisions: When evaluating a loan, 47.8% said the best interest rate matters most, followed by the lowest monthly payment (affordability) at 38.6%. When asked what would most increase their willingness to move forward, 39.8% selected a lower interest rate, and 32.9% selected lower monthly payments.
Borrower Expectations Vary by Generation, but Experience Matters at Every Age
The findings point to a borrower journey shaped by both economics and experience. Consumers are highly sensitive to rates and monthly payments, but many are also comparing multiple lenders and using their earliest interactions to assess whether a provider deserves their business. Digital convenience alone is not enough: the largest group of respondents prefers a digital-first process that still provides access to a person when questions or uncertainty arise.
Click here to continue reading
By The Fintech Times
Click here to read the entire article
Financial services firms have invested heavily in digital compliance infrastructure, automating KYC checks, AML screening and onboarding workflows. Yet the documents those systems produce- account statements, loan agreements, disclosures, application forms- can remain inaccessible to customers who rely on assistive technology, creating a regulatory and reputational gap that sits largely outside the frame of most digital transformation programs.
The argument, laid out in a thought-leadership piece by Continual Engine, a digital accessibility and document-remediation firm, is that a visually compliant document is not necessarily an accessible one. A multi-column statement may render correctly on screen while presenting a scrambled reading sequence to a screen reader. A scanned agreement may contain image-based text that optical character recognition has not properly structured. A loan application may have unlabelled form fields that prevent independent completion. None of these failures are visible during a standard quality-assurance check.
Where accessibility breaks in a compliance workflow
The piece identifies seven stages at which barriers can enter the document lifecycle: authoring, generation, conversion, publication, distribution, review and archiving. A source template built without accessibility tagging will propagate that deficit through every downstream step. Document-generation systems may strip heading hierarchies or flatten table structures during PDF conversion. Legacy document libraries may sit in repositories without having been evaluated against any accessibility standard.
The proposed remediation logic is tiered: prioritise documents by customer impact and volume rather than age, embed accessibility checks into existing quality-assurance gates, and use automation for scale while reserving human review for complex or contextually ambiguous content. The framework is pragmatic rather than prescriptive, and is not tied to a specific regulatory standard, though the obligations it implies are real.
Regulatory read-across
The regulatory pressure here is real and building. In the UK, the Equality Act 2010 requires reasonable adjustments for disabled customers, and the FCA‘s Consumer Duty, which came into full force in July 2023 for open products, explicitly requires firms to support customers who have characteristics of vulnerability, including those with disabilities, in accessing information effectively. The FCA has signalled that Consumer Duty assessments will look at the entire customer journey, not just the transactional interface.
In the US, the Americans with Disabilities Act has been applied to digital financial services through federal litigation, and the Department of Justice issued updated guidance on web accessibility in 2022. The EU’s European Accessibility Act, which member states were required to transpose into national law by June 2025, extends accessibility obligations to certain digital financial services and the documents they produce.
For compliance and technology teams, the practical implication is that document accessibility is no longer a marginal consideration. If a firm’s Consumer Duty assessment or accessibility audit surfaces a pattern of inaccessible statements or agreements, that becomes an evidence trail regulators can act on.
Click here to continue reading
By Henry Meier, Esq., Credit Union Times
Click here to read the entire article
A little more than a decade ago, marijuana banking was one of my favorite subjects to blog about. The Justice Department released the Cole memo in 2013 detailing the circumstances under which it would not prosecute entities involved in the marijuana business, states were moving in the direction of legalizing marijuana and it was only a matter of time, of course, before Congress got around to legalizing the possession and sale of marijuana on the federal level. The continued criminalization of the drug was nothing more than a vestige of a bygone era categorized by “Reefer Madness.”
I was among those who argued that these were good times for credit unions to be among the first institutions to offer banking services to Marijuana Related Businesses. In fact, in states like New York, they were actively being encouraged to do so.
And why not? True, marijuana banking required big investments in staff and technology to comply with heightened compliance requirements, but the expenses were more than outweighed by the profits to be made by opening accounts for marijuana-related businesses.
What a difference a decade can make. These assumptions look as outdated as a Cheech & Chong movie.
On a policy level, there is an increasing recognition that the legalization of cannabis does not come without its flaws. On the political front, momentum for legalization has stalled on the federal level. And perhaps, most importantly, as recent cases demonstrate, the legal complications stemming from state legalization of a product that remains unequivocally illegal under federal law continue to vex depository institutions intrigued by the possibility of providing banking services to MRBs.
In 2014, the New York Times editorial board reflected conventional wisdom when it came out strongly in favor of legalization of marijuana for both recreational and medical purposes. As the paper explained in a Mea Culpa of sorts written earlier this year:
“At the time, supporters of legalization predicted that it would bring few downsides. In our editorials, we described marijuana addiction and dependence as ‘relatively minor problems.’ Many advocates went further and claimed that marijuana was a harmless drug that might even bring net health benefits. They also said that legalization might not lead to greater use. It is now clear that many of these predictions were wrong.”
According to the Times, an estimated 18 million people use marijuana at least five times per week. Annually, 2.8 million Americans experience “cannabinoid hyperemesis syndrome,” or persistent nausea and vomiting. Today’s marijuana is much more powerful than the stuff puffed, but not inhaled, by President Clinton. Like alcohol, it can result in serious health problems. Anecdotally, as someone who lives in a state where recreational use is legal, the constant presence of that unique aroma can be downright annoying. After all, we allow people to drink in their houses, not in the middle of a public street. Given these downsides, is this really the type of activity that credit unions want to be associated with?
Then there is politics. In 2019 the House of Representatives passed the SAFE Act, which legalized banking services for cannabis businesses with bipartisan support. Furthermore, as late as 2020, it even passed the more radical MORE Act, which would effectively legalize marijuana by removing it as a Schedule I drug under the Controlled Substances Act.
Click here to continue reading
By PaymentsJournal
Click here to read the entire article
Banks aren’t struggling to find artificial intelligence use cases—they’re struggling to govern them.
From fraud investigations to dispute resolution, AI is becoming part of the day-to-day work of financial institutions. At the same time, new governance laws in states like Colorado and Texas are introducing new expectations around transparency, documentation, and oversight.
In a recent PaymentsJournal webinar, David Chmielewski, Chief Product Officer and Co-Founder at Quavo and Hailey Windham, Community Lead for Banking at Sardine.ai, along with Jennifer Pitt, Senior Fraud Analyst at Javelin Strategy & Research, explored where these new requirements intersect with existing workflows, and what organizations can do now to build AI programs that are both effective and compliant.
The key is transparency—not just to satisfy regulators, but to maintain customer trust.
Implementing Continuous Governance
One of the main ways AI is currently being leveraged is to help institutions manage the high volume of cases, alerts, disputes, and documentation they are often inundated. These use cases play to AI’s strengths, such as its ability to summarize cases and detect anomalies across vast amounts of data.
In short, AI is helping organizations cut through the noise so they can spend more time on critical tasks. But it isn’t fully autonomous yet.
“We’re using AI today for some of the things that we thought were never possible to automate,” Chmielewski said. “Things like looking at representment documents with lots of evidence and summarizing them; things like customer communication and making sure we can quickly sort through what we’re receiving.”
“We’re also using it for the investigation process, but not without a human in the loop,” he said. “The dream where we’re just handing everything off to AI and it’s doing everything for us is not quite yet realized, but we’ll see if we can get there eventually.”
The challenge is no longer simply implementing AI—it’s governing it. As regulators begin formalizing expectations around AI oversight, organizations must ensure their processes can support transparency and accountability.
For example, the Texas Responsible Artificial Intelligence Governance Act (TRAIGA), which took effect this year, prohibits harmful and intentionally unlawful uses of AI while encouraging organizations to adopt established risk management practices. It also creates a regulatory sandbox where companies can test AI systems under state oversight.
Colorado has taken a similar approach. After enacting the nation’s first broad AI law, lawmakers replaced it with the Automated Decision-Making Technology Act, a more practical framework scheduled to take effect next year.
“I compare this to the recent Nacha explainability requirement,” Windham said. “Those rules weren’t saying don’t use machine learning, they were saying if you’re making a decision that affects customers or your institution’s risk, you need to be able to explain it. We already understand that concept in payments and fraud.”
Click here to continue reading
Micah Zimmerman, Bitcoin Magazine
Click here to read the entire article
A new tri-party lending structure with BitGo lets Kalshi Prime clients borrow against bitcoin to margin perpetual futures.
Kalshi is doubling down on its bid to become the regulated U.S. home for crypto perpetual futures, pairing a new bitcoin-backed lending arrangement with digital-asset custodian BitGo alongside a distribution deal that will put its perpetual contracts in front of Webull’s more than 6 million customers.
Bloomberg first reported Wednesday that customers of Kalshi Prime, the company’s U.S.-registered futures commission merchant, will be able to borrow against digital assets held at BitGo and use the proceeds to fund margin positions on perpetual futures traded on Kalshi’s main exchange.
Under the tri-party structure, loans will be issued by Kalshi Katalyst, a lending affiliate of Kalshi Prime, and secured against assets held at BitGo Bank & Trust, the firm’s federally chartered trust bank.
Eligible collateral will include bitcoin, ethereum and stablecoins deemed compliant with the GENIUS Act, with additional custodians expected to join Kalshi’s network over time.
Prime CEO Jeff Bandman told the outlet the product was designed with crypto-native traders in mind, including those already active on unregulated offshore perpetuals venues and large holders who would rather not sell their bitcoin to fund futures positions.
He also pointed to unexpected demand from businesses, such as Latin American firms that run their operations on U.S. dollar stablecoins.
The move targets a segment where the company has acknowledged a structural disadvantage against Polymarket, its offshore, blockchain-based rival, which has long catered to crypto whales and trading firms that prefer to keep their capital in digital assets. The two platforms have been racing to build out perpetuals since the spring.
Webull debuting crypto-linked perpetual futures via Kalshi rails
The BitGo arrangement landed a day after Webull announced Tuesday that eligible U.S. customers will be able to trade perpetual futures on its platform beginning in November, starting with bitcoin and a handful of other crypto assets.
Click here to continue reading
Alexei Alexis, CFO Dive
Click here to read the entire article
Incidents disclosed by OpenAI and Anthropic expose how AI models can behave in unintended ways, creating new challenges for finance chiefs.
Recent incidents involving artificial intelligence agents have complicated the technology’s rapid rise, exposing risks for companies as they give autonomous systems greater access to sensitive data and business-critical operations.
OpenAI and Anthropic have each in recent months disclosed cybersecurity incidents involving some of their AI models.
The incidents offer a glimpse of what can go wrong when AI systems are given the ability to act on their own. Experts contacted by CFO Dive said agents can pursue assigned tasks in ways that exceed their intended limits, underscoring the need for companies to assess risks and safeguards before giving them access to critical systems.
“We cannot assume an agent will behave as intended simply because it has been given instructions or passed an initial safety test,” said Navrina Singh, CEO and founder of AI governance platform Credo AI.
How agents cross the line
An AI agent refers to a system or program that is capable of autonomously performing tasks on behalf of a user or another system, according to IBM.
A central problem is that an AI system may pursue the stated goal without following the method people expected. Researchers call one form of this behavior “reward hacking,” in which a model finds a shortcut to achieve its objective rather than completing the task as intended.
Matt Pearl, director of the Strategic Technologies Program at the Center for Strategic and International Studies, a policy research organization, said agents can bypass controls as a result of “relentless goal optimization,” exploiting software bugs and other vulnerabilities along the way.
The risk grows when task instructions are vague, permitted actions are not clearly defined or the system lacks a safe way to stop when it encounters an obstacle. An agent can keep searching for ways to complete a task, even when that means bypassing a restriction or taking an action its operator did not anticipate.
What went wrong in testing
The incidents disclosed by OpenAI and Anthropic show how model behavior can combine with technical weaknesses in the environment.
On July 21, OpenAI disclosed that certain AI models it developed were behind an “unprecedented cyber incident” affecting Hugging Face, an open-source AI platform for developing and sharing models.
Click here to continue reading
By FintTech Global
Click here to read the entire article
As AI reshapes financial services, compliance is moving beyond interpreting rules and managing controls. The challenge is increasingly one of engineering: translating regulatory obligations into systems that can adapt, act and demonstrate accountability.
Compliance has traditionally relied on people interpreting rules, managing controls and keeping pace with regulatory change. But as financial institutions grow more complex and AI becomes embedded in their operations, the limits of this approach are becoming harder to ignore. The challenge is no longer just understanding what the rules demand, but building the systems and processes to put them into practice consistently.
This is bringing compliance closer to engineering, where controls must be designed, tested and maintained rather than simply documented. For the RegTech industry, the question is whether this shift will fundamentally change how financial institutions build and manage their compliance functions.
In a new four-part RegTech Analyst Series, the focus shifts onto The Architecture of Compliance: Rebuilding RegTech for the AI era. This series examines compliance in the AI age, and what firms need to be paying attention to.
In the first part of a two-part series of part one we speak to key industry thought leaders to gauge their views.
Compliance: becoming a tech function?
Is compliance becoming a technology function? In the view of Areg Nzsdejan, CEO of Cardamon, increasingly, this is true.
“Turning a regulatory obligation into something a business can consistently execute requires structured data, workflows, controls and testing. Those are engineering problems, and compliance teams need to be involved in how they are solved,” he said.
The judgement, in his view, still matters hugely, as someone must decide what an obligation means for the firm and whether the resulting control is appropriate.
He added, “If that interpretation lives in one person’s inbox, every team ends up reconstructing it. Good infrastructure lets the business apply it consistently and revisit it when things change.”
Meanwhile, Zurab Kotaria, CEO of Identomat, sees that compliance is becoming increasingly tech-enabled but wouldn’t say it’s becoming purely a tech function.
“What is changing is the way compliance is delivered,” he said. “As businesses operate across more markets, regulations become more complex, and fraud becomes increasingly sophisticated, manual compliance processes simply cannot provide the speed and scale organisations need.”
Click here to continue reading
By Melina Druga, Financial Regulation News
The Federal Reserve Board recently released the results of the 2025 Survey of Consumer Finances, a representative picture of what Americans own, how and how much they borrow, and how they bank. It provides information on the economic conditions of American families.
The board also issued a summary report, examining changes in income, net worth, assets, debt, and financial vulnerability. When comparing the 2022 and 2025 surveys, most families experienced moderate increases in income and net worth, but an increasing subset of families have been experiencing financial stress.
Key findings include:
- Real median family income rose 7 percent surveys to $82,200 while real mean family income fell 6 percent to $145,200.
- Real median net worth rose by 2 percent to $215,900 while real mean net worth rose by 7 percent to $1.24 million.
- For families that owned a home, the median net housing value rose to $230,000.
- Retirement plan participation was up slightly to 65 percent.
- Participation in the stock market declined slightly from 58 percent in 2022 to 56 percent in 2025.
- The fraction of families with any type of debt remained about stable at 77 percent.
- The fraction of families with debt payment-to-income ratios greater than 40 percent increased from 6.5 to 8.6 percent.
Aaron Passman, CreditUnions.com/Callahan
Ghosts and goblins are one thing. Fraudsters, cybercriminals, and evolving threats are another. Explore how credit unions are strengthening defenses, balancing risk and innovation, and protecting members in a fast-changing landscape.
Spooky season is here, but it’s a little bit different for credit union leaders.
Ghosts, ghouls and goblins? Not scary enough. Credit union cybersecurity and fraud? Now that’ll keep a credit union leader up at night.
In honor of Cybersecurity Awareness Month, this week CreditUnions.com is all about cyber safety, fraud prevention, and more. In the days to come, keep your eyes peeled for:
- How layered defenses help members separate legitimate requests from potentially costly threats.
- A Q&A with the C-level leader whose legal background informs TruWest Credit Union’s approach to innovation, compliance, and cybersecurity.
- Why your credit union needs an “ethical hacker” on staff.
- Plus, test your cybersecurity knowledge with the latest Callahan quiz.
As always, now it’s your turn. How is your shop beefing up credit union cybersecurity? How has the threat landscape changed at your institution? What’s keeping you up at night and how are you responding? Drop us a line, and we might feature your story on CreditUnions.com.
Let’s get to work.