Gabrielle Saulsbery, Banking Dive
Click here to read the entire article
Bastion Platforms Trust Co., Agora National Trust Bank, and Catena Trust Bank applied for charters in March, April, and May, respectively.
The Office of the Comptroller of the Currency conditionally approved three national trust charters Friday, including de novos Agora National Trust Bank and Catena Trust Bank, along with Bastion Platforms Trust Co., which sought to convert its state charter to a national license.
The three conditional trust banks-in-organization have been waiting to hear back from the regulator since they submitted their applications in April, May and March, respectively. They join nearly a dozen firms that have nabbed a conditional national trust charter – which allow entities to manage assets and act as fiduciaries, but not to take demand deposits or make loans – since late last year.
Bastion white-labels stablecoins for other firms, as well as oversees custody of reserves and customer wallets. Agora is the issuer of AUSD, a stablecoin first issued in August 2024.
Catena Labs, for its part, is developing financial infrastructure for AI agents, creating what founder Sean Neville has called an “AI-native bank” – something of which stablecoins, he said, would play a big part in the growth story.
Bastion founder Nassim Eddequiouaq wrote in a LinkedIn post Friday that, when he started the company, he expected stablecoins to eventually become core financial infrastructure.
“But for the world’s largest enterprises and financial institutions to adopt them, that infrastructure would need to meet the regulatory standards they already expect from their banks,” Eddequiouaq wrote.
“Stablecoins are moving into the financial mainstream, but institutional adoption depends on infrastructure that can meet an institutional standard,” he wrote. “We made the decision early to build Bastion for that standard. Today is an important validation of that decision, and we’re just getting started.”
Spokespeople from Catena and Agora did not immediately respond to requests for comment on their own conditional approvals.
Full approvals are subject to the satisfaction of conditions set forth by the OCC.
Bastion must maintain a minimum of $6 million in tier 1 capital. At least $3 million or 50% of its tier 1 capital (whichever is greater) must be held in eligible liquid assets for its first three years of operation, according to the OCC.
Click here to continue reading
By Stefan Dasic, Malware Bytes
Click here to read the entire article
Phishing follows whatever people want at the moment, and right now that includes AI subscriptions they don’t have to pay for. We recently uncovered a new variation on this theme: A fake Claude Max giveaway that uses a convincing Google sign-in window to steal login information.
Claude’s paid plans start at $20 a month and cost considerably more for higher usage limits, while free accounts have stricter limits. That makes the promise of a free upgrade an attractive lure.
Microsoft reported in June that it had seen a growing number of phishing, malicious advertising, and search-based campaigns impersonating services such as ChatGPT, Claude, DeepSeek and Copilot. Some claim that a payment has failed and send you to a fake checkout. Others offer an app download that installs malware.
The campaign we found takes a different approach. There is no form to collect card details and no download. Instead, it offers a free upgrade and asks you to sign in with your Google account.
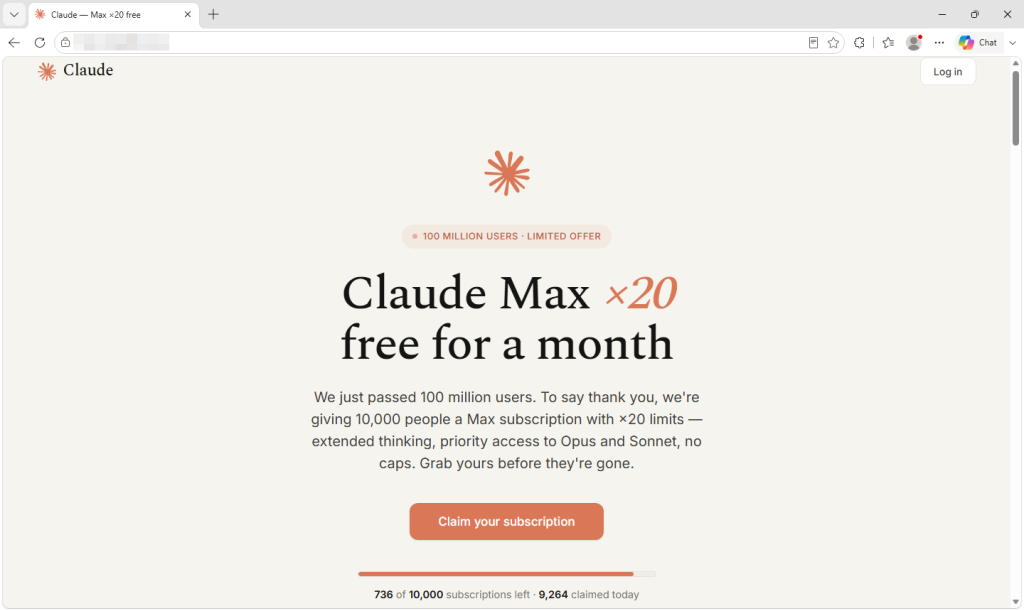
What the page shows you and what it collects
The site announces that Anthropic has passed 100 million users and is thanking people by giving away 10,000 free one-month subscriptions to Claude Max, its highest-usage plan.
The presentation is careful, down to the real logo and colors, invented five-star reviews, and a long footer whose links lead almost entirely to genuine Anthropic pages. This is probably the most effective trust signal on the site, and it cost the operator nothing.
A counter claims that fewer than 750 of the 10,000 slots remain, dropping by a few every several seconds. Nothing is actually being counted. The number is generated inside your browser and resets when you reload the page, so every visitor sees the same manufactured shortage.
The frequently asked questions repeatedly promise that no payment details are needed. That part is true, which helps make the offer persuasive. Many people associate scams with requests for card details, and this page never asks for them.
What it wants instead is your Google login. Two sign-in options appear, but only one works. The Apple button produces a pre-written notice saying that the method is temporarily unavailable. The email box discards whatever you type into it and triggers the Google button instead. Every route leads to the same place, and the prize is far bigger than the lure suggests.
A Google account can provide access to email, documents, and the password-reset messages for other accounts. If you use Google to sign in to Claude, it could also give the criminals a route into your Claude account. Paid AI accounts are valuable in their own right because their usage allowances cost money. Last month, our research covered infostealers hijacking Claude accounts and using the victims’ paid allowances.
Click here to continue reading
By Tom Nawrocki, Payments Journal
Click here to read the entire article
For an industry that operates across 50 states, navigating prepaid regulation can feel like navigating 50 different rulebooks. With most regulatory action happening at the state rather than federal level, retailers and card manufacturers must keep up with a growing number of requirements—and ensure their products comply with the states with the strictest rules.
Javelin Strategy & Research’s 2026 Prepaid Regulatory Update: States Focus on Fraud and Cash-Outs report examines the legislative changes that affected the industry over the past year and what may be ahead as more states step up efforts to regulate the gift card industry.
“It’s really critical that those people who are interested in what’s happening on a regulatory basis understand it state by state,” said Jordan Hirschfield, Director of Prepaid at Javelin Strategy & Research and co-author of the report.
Two Paths Toward Fighting Fraud
A number of states are working to enhance fraud protection, but they are taking different approaches. Some are targeting the perpetrators, while others are focusing on the products themselves, requiring packaging designed to prevent bad actors from tampering with cards.
The Retail Gift Card Association favors measures that target perpetrators, viewing them as a way to punish the crime rather than impose costs on businesses to prevent it.
“The technology behind how to make a card secure is technically difficult,” said Hirschfield. “Getting the supply chain set up so that not just the card itself but the software that goes behind that card and the packaging that goes on top of the card, all conform to a certain state’s rules can be difficult and costly. At what point are you taking the benefit away from the consumer to try and prevent a crime instead of punishing the crime itself?”
Changes to State Laws
Maryland has led the way on regulations governing anti-fraud packaging and continues to have some of the most stringent requirements. Other states, however, have followed suit.
“New York is proposing to conceal all numbers on the card,” said John Vogl, Analyst and Content Specialist at Javelin, and co-author of the report. “This becomes a de facto national law just because New York is so big that all the issuers and designers would have to follow New York’s rules nationwide.”
If New York’s law passes, manufacturers would have just 180 days before it takes effect, leaving limited time to adapt. Either way, the potential changes create challenges not only for retailers sponsoring gift card programs, but also for card and packaging manufacturers. Multiple parties across the supply chain would be affected.
Meanwhile, California is raising its cashback limit to $15, meaning gift cards with balances of $15 or less can be redeemed for cash.
“This opens up the opportunity for more theft and fraud because if someone can compile enough cards with close to $15 on them, they stand to receive a decent amount of money,” said Hirschfield. “Five is a more common number—it’s hard to spend less than $5 in a lot of places, so being able to cash out the remaining balance is good customer service, regardless of if it was a rule. Once you get beyond $10 you might be inviting bad actors to participate. It also means you need more cash on hand, which might put your staff at risk.”
As a result, retailers operating in California need policies for that state that differ from those used at other locations. For national retailers, that could mean different employee training programs, applications, and even requirements for how much cash each store needs to keep on hand.
Opportunities in Gambling
While much of the regulatory activity is focused on gift cards and fraud prevention, regulation is also creating new opportunities for prepaid in other areas. One of those is gambling, where prepaid products are becoming an increasingly relevant way for consumers to fund betting accounts.
The number of states approving sports wagering appears to have plateaued, and the amount of money wagered has declined in authorized markets, partly as consumers turn to newer, less regulated platforms such as Kalshi and Polymarket.
Click here to continue reading
Eric J. Troutman, Troutman Amin, LLP, National Law Review
Click here to read the entire article
The FCC has just revealed the critical revisions to its TCPA revocation/opt out rules it has been working on– an they are massive and wonderful for callers and consumers alike.
The new rules align with common sense and assure a consumer’s expectations are followed and that a business can swiftly honor a valid revocation effort.
The new rule–which is set to be adopted at the September open meeting– will provide as follows:
- When a consumer opts out of an informational text campaign the opt out only impacts that specific type of informational message– not all messages as the “nuclear” rule was set to require;
- When a consumer opts out of a marketing message, however, all future marketing from that entity must cease; but
- Businesses can set an “exclusive” means to opt out (either via keyword or keypunch response) and need not honor any revocation request made via a different method.
Absolutely huge changes here. And critically important for businesses to understand how these rules will play out in the real world.
A little more color on each of these rules.
As to the “informational” message limitation callers may now “interpret a revocation request as applying only to the specific category of informational robocalls to which the revocation was directed and not all robocalls.” See ruling par. 10. Although the Commission uses the phrase “robocall” it applies equally to automated texts to the extent those messages are covered by 227(b). See fn 1.
However the Commission is clear that a response to a “marketing” message creates a revocation to all future marketing: “Revocation requests made in response to robocalls that contain an advertisement or constitute telemarketing revoke consent to all future robocalls containing an advertisement or that constitute telemarketing from that caller.” Notice this is framed as a CALLER specific revocation requirement– but one wonders whether it might extend to a party the caller is calling on behalf of. This is especially true as the commission goes on to state “we remind telemarketers that our rules require that a residential subscriber’s do-notcall request shall apply to the particular entity making the call (or on whose behalf a call is made), as well as affiliated entities if the consumer reasonably would expect them to be included. par. “Hmmm.
The best news for callers, however, is definitely the ability to use a designated opt out mechanism and to honor only revocations made through that opt out means: “Using an automated, interactive voice or key-press activated opt-out mechanism in response to a robocall, (2) using specific standardized words in response to an incoming text, and/or (3) using a website or telephone number provided by the caller to process opt-out requests, so long as the caller clearly and conspicuously discloses the designated method for revoking consent on the call or in the text. Callers that designate any of these three exclusive means to revoke consent will not be required to process revocation requests made by any other means.” Just fantastic–and common sense–stuff here.
Click here to continue reading
By Ken McCarthy, Tyfone
Click here to read the entire article
At a Philadelphia industry summit, executives and regulators described a cautious approach to artificial intelligence: use it to make employees more productive, but keep people in control.
For Jason Mertz-Prickett, the chief executive of a $92.7 million-asset credit union in California, artificial intelligence is less about chasing the newest technology than finding ways to give a small institution more time.
Upward Credit Union in Burlingame has deployed Microsoft Copilot to managers and selected employees, while Mertz-Prickett and the chief operating officer are the only employees permitted to use ChatGPT. The tools help with tasks including reviewing policies, drafting communications and developing member messages.
The goal, Mertz-Prickett said Wednesday at the National Association of State Credit Union Supervisors’ annual State System Summit in Philadelphia, is not to eliminate jobs. It is to make employees more efficient and free them to spend more time with members.
“Our employees love it, our board loves it,” he said during a session titled “From Innovation to Implementation: What Actually Works.” The technology has allowed employees to spend more time working directly with members while producing what he described as a stronger work product.
For Upward, the experiment reflects a broader challenge facing smaller credit unions. Institutions do not necessarily need to be first to adopt every new technology, Mertz-Prickett said. They need to figure out how to use tools already available without exposing member information or taking on risks they do not understand.
That caution has shaped Upward’s approach from the beginning.
Mertz-Prickett said he took an artificial-intelligence policy to the credit union’s board about three years ago, before Upward was using Copilot or ChatGPT in its operations. The move was intended to establish clear rules before the technology became embedded in the institution’s work.
Among those rules: Employees cannot put proprietary or nonpublic information into the AI platforms. Any material intended for members must be reviewed by a senior manager before it is sent out.
The policy also gave employees a common understanding of what they could and could not do with the technology as Copilot was gradually introduced, Mertz-Prickett said.
Click here to continue reading
By Steve Cocheo, The Financial Brand
Click here to read the entire article
A multi-billion-dollar new lending opportunity, with the potential for establishing deep and long-term new consumer relationships, arrived in early July, courtesy of the “Big Beautiful Bill.”
How many lenders will actually take advantage of this development? That remains to be seen: Experts agree that student lending is not something neophytes can (or should) get into quickly nor at scale.
Need to Know:
- Washington’s student loan portfolio stands at around $1.7 trillion, according to the Education Department. Under the latest changes, a big chunk of that will migrate over time to the private sector.
- Student lending is a political football, and future changes at the White House may demand nimble planning on lenders’ part.
- For a private lender, an education loan, especially for a graduate or professional degree, is in part an investment in the future earnings potential — and repayment ability — of a degree in a particular field and from a particular school.
- What it’s all about: The new opportunity results from major changes made to federal student lending programs by last year’s law and implemented by the Department of Education.
The bill, which picked up the official moniker, “Working Families Tax Cuts Act” along the way, kills a major federal graduate student loan program as of this year, with a phase-out for current borrowers. In addition, more-stringent limits on an individual’s federal student debt borrowing overall are taking effect.
The Trump administration has argued that these steps will force colleges and universities to contain their costs and make education more affordable, while getting the government further out of the student lending business.
Key insight: In practice, the federal policy shift is pushing a huge amount of credit demand into the private sector.
“There are going to be a lot more students who have needs and those needs will be unmet by federal programs,” says Joshua Turnbull, SVP and consumer lending business leader at TransUnion. “That creates an opportunity for private lenders to enter the fray.”
Chris Hahn, head of consumer healthcare and student lending at KeyBank, puts the sea-change in perspective:
“The federal government doesn’t underwrite credit quality. There is no use of credit scores nor debt-to-income ratios. There is no, ‘What is your credit profile? What is your past performance?’ But for private lenders, and traditional bank lenders, credit quality matters.”
About half of the demand that’s coming will be readily bankable, Hahn estimates. The other half? Under current conditions, not so much.
Click here to continue reading
By PaymentsJournal
Click here to read the entire article
Every payment tells a story about a member’s financial life. The challenge for credit unions is that more of those stories are now being told somewhere else.
Buy now, pay later (BNPL) has transformed from a checkout convenience into a growing part of how consumers manage cash flow, budget, and make purchasing decisions. While these installment options create flexibility for members, they also create new relationship opportunities for the financial providers that offer them—opportunities many credit unions have yet to capture.
In a recent PaymentsJournal podcast, Adam Hodz, Managing Vice President of Payment and Channel Solutions at Velera, and Ben Danner, Senior Debit Analyst at Javelin Strategy and Research, discussed the evolution of BNPL usage and how credit unions can differentiate themselves by integrating BNPL capabilities into their offerings.
At its core, BNPL is about giving consumers more choice. That makes it more critical for credit unions to deliver a comprehensive suite of solutions that keeps them at the center of members’ financial lives.
From Financing to Money Management
In its early stages, many viewed BNPL as a modern form of layaway, allowing consumers to split larger purchases into manageable installments. While that use case still applies, today’s BNPL landscape has evolved beyond that original concept.
“It’s an evolution from a financing option for large purchases into everyday money management,” Hodz said. “The buy now, pay later conversation is shifting from, ‘Can consumers finance and purchase?’ to consumers expecting flexibility in all transactional situations. Whether it’s online or in-store, they want that flexibility.”
Mounting evidence shows that a significant portion of BNPL transactions are used for everyday purchases under $30, and some consumers rely on these products on a weekly basis.
As installment payments become a common tool for budgeting and cash flow management, credit unions that offer only traditional card products risk falling behind evolving member expectations.
“Smoothing out routine expenses, managing short-term cash flow, and helping to create a little more predictability in their budgets. If those options are available only through fintechs or merchant-driven providers, credit unions are going to risk being on the outside looking in,” Hodz said. “It’s incredibly important to offer those flexible payment channels that consumers and members are looking for to help manage their money.”
Payments Are Relationship Moments
One of the key reasons BNPL has become essential is that it allows credit unions to maintain a more complete view of member behavior.
Today, many BNPL experiences occur outside the credit union ecosystem through fintechs and merchants. This not only limits visibility into member activity but also creates risk that members will build stronger relationships with external financial services providers.
As more transactions move beyond a credit union’s reach, institutions lose opportunities to engage members through loyalty programs, personalized offers, and targeted promotions. These touchpoints are essential ways for credit unions to strengthen relationships and position their digital banking experience as the preferred destination for financial activities.
Click here to continue reading
By Shyam Pradheep, FinRank/Financial Brand
Click here to read the entire article
Ask a credit union executive whether AI will matter to their institution and you will get a confident answer. Ask what data that AI would actually run on, and the confidence tends to thin.
In a faculty-sponsored independent study I conducted at Stanford Graduate School of Business, 78% of the 46 credit union executives I interviewed said AI will be a source of competitive advantage. The activity behind that belief varied enormously. Some institutions were using generative AI for internal drafting and summarization; others had moved into real automation or production machine-learning use cases. But one pattern in the responses should give banking leaders pause.
Reality check: Executives rated their institutions’ AI readiness an average of 3.3 out of 5. They rated frontline data visibility 3.0, and the degree to which their workflows actually support data-driven work only 2.8. More telling than the gap itself was how loosely those numbers held together: self-assessed AI readiness had only a weak relationship with the strength of the underlying data foundations, a correlation of r = 0.23. Twenty-four of the 46 executives, more than half, rated their AI readiness above the average of their own data-visibility and workflow scores.
I do not read that as executives misunderstanding AI. I read it as a definitional problem. Ask most institutions how AI-ready they are, and they answer a question about access: Do we have approved tools? Have we run a pilot? Is there a policy? Are our vendors shipping AI features? Has someone shown the executive team a demo that landed? Those are all evidence that an institution is experimenting with AI. None of them is evidence that it can use AI well.
AI Readiness Has a Measurement Problem
An institution can deploy an AI assistant, buy an AI-enabled vendor product, and stand up an internal working group without becoming meaningfully more capable of putting intelligence to work across the business. The distinction is easy to miss, because modern AI tools make experimentation unusually cheap. A department can start using a model in days. A vendor can bolt an AI feature onto its product without touching the institution’s underlying architecture. And an executive team can watch a polished demonstration long before the data required to reproduce that experience reliably exists anywhere in its own environment. The result is a dynamic that’s all too familiar with AI that looks mature at the interface while remaining immature at the operating layer.
Consider what a genuinely AI-ready institution should be able to do. It should be able to identify the relevant information about a member. That information should be clean and consistent enough to trust. Systems should be able to reach it without extensive manual stitching. A governed workflow should be able to act on it. And someone should be able to say what business outcome the AI is meant to improve and be accountable for measuring whether it did. That is a considerably higher bar than having access to a model.
Key insight: This matters more in financial services than in most industries, because the AI problem here is a different shape. The value is not primarily in asking a general-purpose model questions it already knows how to answer. The larger opportunity is connecting intelligence to proprietary institutional information and to real operating workflows and that is precisely where most institutions are weakest.
The Real Bottleneck Is Data That Can Move
The most consistent finding in my interviews was not that credit unions lack data. It was closer to the opposite: they have enormous quantities of it. What they lack is a unified, accessible foundation that lets people and systems act on that information while it still matters.
Click here to continue reading
By Russell Brandom, TechCrunch
Click here to read the entire article
As AI makes it easier to fill forms and file complaints, public services around the world are seeing enormous jumps in applications and other requests.
In the United Kingdom, complaints to the housing ombudsman more than doubled since the introduction of ChatGPT, rising from 2,600 in 2022 to just over 7,000 last year. The United States’ Consumer Financial Protection Bureau (CFPB) saw 5x growth in complaints over the same period. There were similar jumps in Brazilian judicial petitions and German parliamentary petitions.
Researcher Chris Schmitz is tracking this rise as part of a broader trend he called “agentic flooding.” In a paper set to be presented next month at the AI Ethics and Society conference, he looks at 84 different cases of potential flooding across 11 jurisdictions, finding broad evidence that AI tools are changing the way people interact with public services.
The harder question is what to do in response. While some of the new filings are clearly adversarial, others are the result of legitimate applicants using AI to file claims that would otherwise be abandoned. While some might see the new applications as AI-generated spam, Schmitz sees it as a rare opportunity to remake social services for the AI era.
Schmitz looked at services ranging from welfare applications to official judicial appeals, but they all have online services that could be accessed by an AI assistant. (The full dataset is hosted here, for reference.) For methodological reasons, Schmitz’s paper stops short of saying AI is directly causing the surge of new applicants. But most of the 84 cases follow the same basic arc, where submissions were roughly flat before 2022, then rose at increasing speed as AI technology diffuses. Crucially, most cases have not seen that growth slow down, suggesting it will likely keep rising for years to come.
For Schmitz, it’s easy to see how the increasing skills and availability of AI would drive increased usage.
“People are finding out that this is something one can do, and incrementally, it is just getting easier to do it … before it might have been a question of a lot of dragging context together and prompting ChatGPT 3.5 very precisely, it may now be a question of just pasting or taking a photo of a letter with your Claude app and getting a pretty good response in one shot,” he said.
The jump in volume is similar to what many bug-bounty services also experienced last year, as companies found their inboxes flooded with low-quality reports generated by LLMs. The reports rarely contained significant security issues, but companies were still obligated to vet the reports as they came in, presenting a significant drain on resources. It’s easy to imagine public services facing a similar problem, as they manage 5x more applicants with the same budget.
Click here to continue reading
By John L. Culhane, Jr., Ballard Spahr/Consumer Finance Monitor
Click here to read the entire article
The Treasury Department’s Financial Crimes Enforcement Network (FinCEN) has issued an Alert “urging financial institutions to detect, prevent, and report suspicious activity connected to fraud schemes targeting student aid programs administered by the Federal government.”
“Every dollar stolen from Federal student aid is a dollar taken from taxpayers and deserving students,” said Secretary of the Treasury Scott Bessent.
“Fraud rings use stolen and fraudulent identities, as well as other tactics, to enroll in educational institutions and unlawfully acquire funds from Federal student aid programs,” according to FinCEN officials. “The schemes not only result in losses to Federal student aid programs, but in some cases, real students face difficulties enrolling in classes because of the number of fraudulently enrolled ‘students.’”
They said that the Education Department has launched an “effort to prevent fraud in Federal student aid programs to protect taxpayers while significantly reducing associated administrative burdens on colleges and universities. [The Education Department and its Office of Inspector General] have consistently worked to detect, investigate, and facilitate the prosecution of fraudsters, as well as to communicate emerging fraud risks associated with Federal student aid and other ED programs.”
In late 2025, ED officials said that it had prevented $1 billion in Federal student aid fraud during that calendar year.
Elaborating on how many of these sehemes work, FinCEN said that fraudsters often steal personally identifiable information to create “ghost students.”
“To create ghost students, fraudsters may illegally obtain Personally Identifiable Information (PII) to impersonate an identity theft victim and pose as a legitimate student,” according to FinCEN. “Fraudsters may also use artificial intelligence or other tools to overcome identity verification by generating fraudulent documents that combine stolen PII with fabricated details, commonly referred to as synthetic identities. Victims whose identities are leveraged as part of ghost student schemes, including minors, are unaware that fraudsters are receiving Federal student aid using their PII.”
FinCEN officials said that in addition fraud rings sometimes use complicit “straw students” to obtain federal student aid. Straw students are individuals who, for a fee, provide their PII to fraudsters, who enroll them at educational institutions and collect financial aid refunds issued in their names.
They added that corrupt staff at educational institutions may also take advantage of their positions to defraud student aid programs by recruiting straw students and managing their educational records.
Click here to continue reading.
By Tara Seals, Dark Reading
Click here to read the entire article
In bad news for financial institutions, online retailers, cryptocurrency exchanges, and people in the dating pool who rely on identity verification to make sure they’re not getting taken for a ride, global fraud gangs are aggressively industrializing their scam efforts.
That’s according to Eric Huber, senior manager for adversary intelligence and disruption at TD Bank, who said that major centers for organized crime specializing in financial fraud (notably in Southeast Asia and West Africa) are bypassing “know your customer (KYC)” rules and other identity-verification methods with an updated AI tool set that offers the ability to build completely believable synthetic identities capable of fooling even advanced AI-enabled behavioral defenses.
His research into fraud cartels dovetails with recent numbers from Interpol, which in March said that, since 2024, the number of fraud-related campaigns it tracks has increased by 54%, fueled by AI. Over the same period, Interpol-supported member countries in more than 1,500 transnational fraud cases lost assets valued at $1.1 billion; it also deduced that AI-enhanced fraud is 4.5 times more profitable than traditional methods.
Speaking from the stage of the AI Summit at Black Hat USA 2026, Huber pointed to a real-world example of the threat landscape: recent updates to three-year-old tradecraft used by Nigerian scam rings called ProKYC, which is a turnkey KYC-bypass kit that defeats document-plus-selfie customer onboarding with convincing forged IDs and deepfaked “liveness” videos.
ProKYC: West African KYC-Bypass Supercharges Its Chances
To show how ProKYC is iterating in concerning ways, Huber first demoed a legacy version of the tool, which takes any photograph and generates a non-existent person using stolen personally identifiable information (PII). It first creates a convincing facsimile of a passport (in the demo, it’s an Australian document), as well as a video showing a person moving their head around, which should satisfy liveness detection. If asked, it can also emulate a mobile camera feed, so the verifier “sees” a live session with the fake person.
“It’s very convincing, and yeah, I’m sure you’re going to see a successful attack at the end,” Huber said. “Are bad guys very pleased? Yes.”
That’s impressive enough, but in the age of deepfake detection and other AI fraud-rooting defenses, this baseline deepfaking isn’t as successful as it once was. So, newer versions sold via Telegram channels offer specifically tailored workflows for a broad target list across crypto-exchanges and fintechs, with new AI-enabled features that can match the verifier’s request flow automatically.
One of the more notable features is auto-generation of “selfie-with-ID” uploads (essentially, a person holding a “real” ID that was just purportedly uploaded for verification, featuring a desk, keyboard, or table in the background for verisimilitude).
“The thing is, if you were defending yourself, how are you going to defend yourself against a perfectly convincing [fake picture supposedly taken in real time]? One of the things you do is you’re going to look at the ID, and [ask for backup verification],” said Huber. “So ProKYC will go ahead and create that selfie, or even emulate the supposed customer taking a picture of the picture on a keyboard or a table.”
Other recent AI-enabled features include automatic geo-tailored EXIF metadata insertion on the fake images to evade origin checks. Thus, a selfie-with-ID picture “taken” in Nigeria can be made to say it was taken in Sydney, in the Australian example.
Click here to continue reading.
By Patrick Sickels, CUSO Magazine
Click here to read the entire article
There exists in the plaintiff litigation world a strategy occasionally referred to as the “edge,” the “hit list,” or more commonly as the “reptile” strategy. Paraphrasing the foundational principle of this strategy, plaintiffs are seeking to trigger a fear response in a juror by framing defendants as dangerous to the public, with the verdict being the only method to protect innocents, and by extension the jurors themselves.
This is very relevant to credit unions and credit union service organizations because privacy and data security lawsuits heavily rely on these tactics to receive favorable, large-dollar verdicts.
Background to the reptile strategy
In the late 2000s, David Ball and Don Keenan published Reptile: The 2009 Manual of the Plaintiff’s Revolution. The strategy borrowed a (since discredited) neuroscience theory that humans have a reptile brain that governs self-preservation underneath the rational and emotional layers.
Although the underlying science itself may have been disproven, the reptile strategy has proven highly effective in litigation. The structure is to create in the minds of the jurors a safety rule that has been violated by the defendant. The final framing is to suggest a monetary verdict favoring the plaintiffs is the only way to ensure the safety of the community.
Reptile strategy also has the advantage of clarity, where jurors are presented with “right versus wrong” or even “good versus evil” arguments. A verdict favoring the defendant is not just wrong but is immoral.
Building the perfect reptile
This strategy is developed in the early phases of litigation, through discovery such as depositions. The goal is to frame the issue at hand where denial of a question’s premise damages the defendant’s credibility, but where answering it affirmatively creates a standard that is impossible for the defendant to meet.
An example would be: “Is a credit union obligated to follow the federal regulations on data security? … And do you agree those regulations are imposed for the safety of the public?”
The goal of this question is to create a trap where a judgment call is turned into an absolute. GLBA regulations are transformed from a regulatory compliance framework into “safety rules” where any violation endangers the jurors. Unless these questions are objected to, nearly all defense witnesses will answer yes to these questions. At that point, the plaintiffs have already won a significant concession, since any potential violation is now a matter of public safety which affects the jurors.
Another powerful strategy is to use contract and policy language against the defendant, by finding absolute language. Trap words include statements such as “never,” “always,” “immediately,” and “highest,” which permit the plaintiff to argue a judgment call is in actuality an absolute standard.
In one pixel tracking case, the plaintiffs noted in their complaint that the defendant’s “privacy policy stated expressly that ‘we never provide advertisers or any other third parties any information that reveals a personal health condition or personal health information.’” The plaintiff went on to say that “sensitive personal information communicated … including health information relating to medical treatments and prescriptions, was disclosed to and intercepted by some of the largest advertising and social media companies in the country…”
Use of the word “never” in a public-facing policy opened the door for an argument framing the defendant as a hypocrite and dangerous to public safety. The plaintiffs ultimately won a monetary settlement award.
Use of reptile arguments
Plaintiffs using reptile strategies will ensure that it is designed to have maximum impact on a potential juror. The kinds of highly persuasive closing arguments will have elements designed to sway jurors away from legal arguments and instead towards abstract notions of morality.
Click here to continue reading
2026 NASCUS Legal Symposium
Stay Current. Get Connected. Be Prepared.
Join us, Nov. 12–13 in New Orleans, as we bring together agency general counsel, credit union counsel, and private practitioners from across the country.
This new 1½-day event is designed to support professional development and meaningful dialogue around the legal issues shaping the credit union system. Through focused sessions and peer exchange, attendees will gain practical insight they can take back to their organizations.
Learn More